

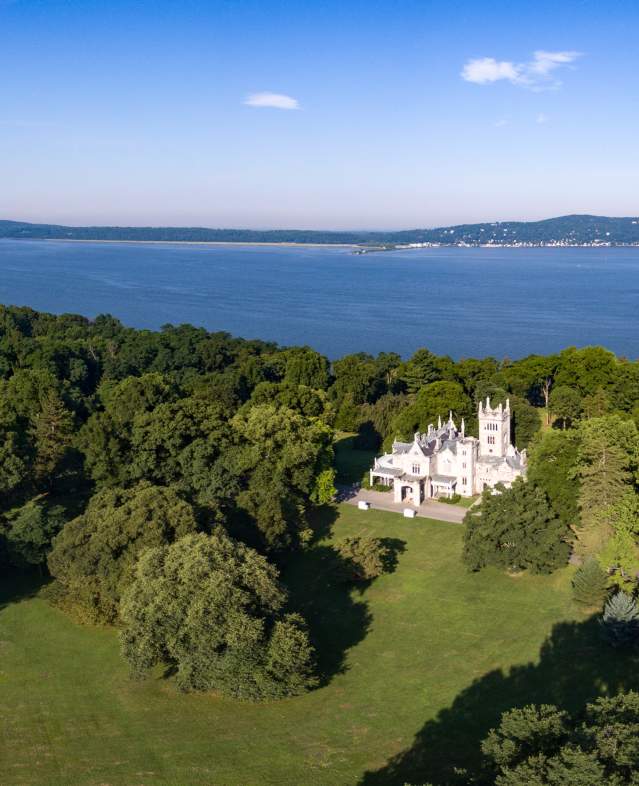
Signature Security Summit | New York | Spring Edition
Prevention remains part of every security program, but most leaders now plan for the moment it isn't enough. This summit brings security leaders together to compare how they detect, contain and recover from incidents, and keep the business running while they do. It's a chance to share what has worked, what hasn't, and what comes next.
Event agenda
Day 1
Day 2
Speakers
Brent Forrest
CISO, Crash ChampionsDr. Lovelie Moore
BISO, Tayota Financial ServicesDana Kilcrease
Chief Information Security Officer, Berkeley CollegeDevon Euring
Head of Operational Risk, iHeartMediaWayne Dennis
OT-CISO, SolventumJim Motes
CISO, RyanCharles Everette
CISO and Chief HIPAA Officer, City of Fort LauderdaleVernetta Dorsey Windsong
Chief Product Security Officer, CarrierAttendees
See attendees
Meet with fellow industry leaders and solve today’s greatest business challenges.
Workshop's & Content Sessions
The Security Chapter NA talk tracks start with resilience and recovery in practice, then cover the areas shaping security planning: AI as both a defence and a risk, identity beyond the employee, supply chain and third-party exposure, deepfake-enabled fraud, governance and the boardroom, security people want to use, and quantum readiness.
Built to Bounce Back: Making Recovery Your Strongest Control
Abstract
It's 2:00 a.m. Your team confirms an attacker is inside your network, and your preventive controls didn't stop them. Within the hour you need answers to three questions. What do we shut down? Who do we call? What do we restore first?
In this workshop you'll work through that hour in small groups with peers, using your own environment as the starting point. You'll pressure-test the parts of a plan that matter most when the clock is running:
- Incident-response and crisis-communication plans.
- Immutable and offline backups.
- Operational technology continuity.
- Supplier contingency planning and cyber insurance.
You'll also decide where business leaders need to be in the room for recovery exercises, and what they need to practice.
Then you'll compare your answers with peers who have been through it. You'll hear what worked, what didn't and where they're investing next.
Key takeaways
- A test for your own recovery plan: how quickly can you detect, contain, recover and keep operating?
- Which resilience investments peers say have earned their place.
- A way to bring executives into recovery exercises before a real incident does.
What Could Your AI Agents Reach? A Practical Look at AI Risk
Abstract
If an attacker manipulated one of your AI agents tomorrow, what could it reach? And who granted it that access?
Your AI exposure now spans models, prompts, training data, plugins and the permissions given to autonomous agents. The World Economic Forum reports that 87% of respondents identify AI-related vulnerabilities as the fastest-rising cyber threat.
This workshop takes five risks in turn:
- Prompt injection and manipulation of agents.
- Sensitive data leaking through generative AI tools.
- Machines with excessive or poorly governed permissions.
- AI-generated phishing, deepfakes and malware.
- "Cost exhaustion" attacks, where attackers trigger heavy use of your public-facing AI services to inflate your costs.
Hold each one up against your own environment and see where it lands.
Key takeaways
- A map of your AI attack surface: models, prompts, training data, plugins and agents.
- Agent permission controls you can put in place before agents scale.
- Where AI strengthens your defense, and where a human stays accountable.
Panel Discussion - Who's Really Logging In? Securing People, Machines and Agents
Abstract
Fewer than 1% of the identities in a typical enterprise now belong to a person. Palo Alto Networks' 2026 research puts the average at 109 machine identities for every human one, up from 82 the year before. Every new agent, app, device and service account needs to authenticate too.
So how much of your identity program was built around that 1%?
This panel brings together security leaders who have extended identity controls well beyond employees. Gartner forecasts that by 2028, 25% of corporate security breaches could stem from AI-agent misuse involving unmanaged machine privileges and existing credential practices.
Panelists will share how they handle phishing-resistant authentication, short-lived credentials, least-privilege access and continuous verification across people and machines. They'll tell you which they started with, what slowed them down and what they would sequence differently.
Bring your own constraints, whether that's legacy systems, budget or a team that can't do everything at once, and put them to the panel.
Key takeaways
- How peers are extending identity and access management to applications, service accounts, devices and AI agents.
- Which controls delivered the quickest wins, and which took longer than expected.
- A sequence for your own identity work, based on what panelists did first.
Harvest Now, Decrypt Later? Map What Matters Before It Does
Abstract
Which data does your organization hold today that will need to stay confidential for many years? An adversary can collect that data in encrypted form now and decrypt it once quantum systems are powerful enough. This is the "harvest now, decrypt later" risk.
Quantum systems can't yet break public-key cryptography at scale, but the World Economic Forum reports that 37% of respondents expect quantum technologies to affect cybersecurity within 12 months. The task today is migration planning, not reacting to a confirmed breakthrough.
Expect a peer working session that turns quantum risk into a prioritized plan for your own organization.
Key takeaways
- A clear view of which data assets carry long-term confidentiality risk, and what that means for the business.
- A way to position quantum readiness as an investment decision for your executive team and board.
- A position on how quantum readiness should shape supplier and procurement decisions.
Keynote - Real Voice or Face. Real Request? Protecting Payments, People and Reputation
When a request looks and sounds exactly like your CFO, what counts as proof? And who in your organization decides?
Generative AI makes voice cloning, video impersonation and business email compromise cheaper to produce. These attacks exploit trust and urgency rather than technical weaknesses, which puts finance, customer service, recruitment, senior leadership and public communications in scope alongside IT.
This keynote opens up the questions that sit with leaders. Where should verification sit for payment changes, credential resets and sensitive disclosures? What does awareness training look like when the usual giveaways are gone? How much friction is the business willing to accept?
Bring your own view and test it against the room.
Key takeaways
- A view of where trust-based decisions create the most exposure in your organization, from payments to hiring to public communications.
- A way to weigh verification against speed, so protection doesn't slow the business down.
- A framing for taking deepfake risk to your executive team and board, including who should own it.
Panel Discussion - Turning Cyber Governance into Board-Ready Evidence
Abstract
A board member or regulator asks: who owns this risk, and how do you know it's controlled? How long would it take you to answer with evidence?
As AI, cloud services and supply-chain dependencies become part of critical business processes, boards and regulators want proof that cyber risk is governed. A list of tools you've bought doesn't provide it.
This session brings together leaders who answer those questions regularly. They'll share how they:
- Document cyber-risk ownership.
- Report incidents faster and more consistently.
- Assess AI risk and control how AI is used.
- Evidence supplier oversight.
- Build board reporting around business impact rather than technical activity.
Come with the question you'd least like to be asked, and hear how others would answer it.
Key takeaways
- A way to define and document who owns each cyber risk at executive level.
- How to move board reporting from security activity to business impact.
- A clearer view of the evidence boards and regulators now expect, including AI use and supplier oversight.
Fix What Matters First: Risk-Based Exposure Management in Practice
Abstract
Your scanner reports thousands of findings, and your team can investigate only a fraction of them this quarter. Which do you fix first, and which could a machine fix for you?
AI and automation can now discover exposed assets, prioritize vulnerabilities and remediate weaknesses. Gartner lists autonomous exposure remediation among its strategic technology trends for 2027. Automation also carries risk: an incorrect change could disrupt production, and attackers may try to manipulate the data your security tools rely on.
Key takeaways
- A way to prioritize exposures by exploitability and business criticality.
- A starter framework for what to automate and what needs human sign-off.
- Safeguards for production systems and the integrity of your security data.
Our Previous Speakers

Brent Forrest
CISO, Crash Champions
Dr. Lovelie Moore
BISO, Tayota Financial Services
Dana Kilcrease
Chief Information Security Officer, Berkeley College
Devon Euring
Head of Operational Risk, iHeartMedia
Wayne Dennis
OT-CISO, Solventum
Jim Motes
CISO, Ryan
Charles Everette
CISO and Chief HIPAA Officer, City of Fort Lauderdale
Vernetta Dorsey Windsong
Chief Product Security Officer, CarrierWhy attend?
Thoughtful Connections. Meaningful Impact.
Curated
Discovery
Intentional conversations that surface real opportunities.
Meaningful Connections
The right people, in the right room, at the right time.
Applied
Insight
Perspective grounded in real execution.